
Create and manage policy rules
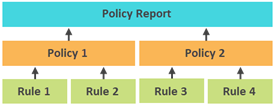
Rules are used to ensure that device configurations comply with policies. Each rule defines a search string that either must or must not be present in a configuration. For example, a rule can specify that configurations cannot include the read-only community string "public."
Each rule applies to a specific set of device configurations, which are selected at the policy level.
To learn how rules, policies, and policy reports work together, see About NCM policy reports.
See the following sections:
Create a rule
Complete the following tasks to create a rule:
-
Do one of the following:
-
Define the search string using basic matching.
Use basic matching if you want to search the entire config for one string.
-
Define search conditions using Advanced Config Search.
Use Advanced Config Search if you need to build conditions using multiple strings, or limit the search to a block of the config.
-
Task 1: Add and identify the rule
-
Click My Dashboards > Network Configuration > Compliance.
-
Click Manage Policy Reports.
-
Click the Manage Rules tab.
-
Click Add New Rule.
-
Name the rule, and enter a description.
-
Select the Alert Level that indicates the severity of violating this rule.
You can customize alert level descriptions.
-
Select an existing folder to store the rule in, or select New folder and enter a folder name.
Task 2: Define the search string
Define the search string in either of the following ways:
- Use basic string matching to search the entire config for one string. You can enter a simple string or a regular expression.
-
Choose Advanced Config Search if you want to:
-
Define a search string that includes conditions (multiple lines connected by
ANDorORoperators). -
Specify a block of the config to search, instead of searching the entire config.
See Examples of search string conditions for information about defining conditions.
-
Define the search string using basic string matching
-
Specify whether the rule triggers an alert when the string is found or when the string is not found.
-
Specify the string to search for. You can enter a simple string or a regular expression.
By default, a simple string can not include the wildcard characters ? and *. To use wildcards, do one of the following:
-
Enter a Regular Expression.
-
In NCM 2023.1.1 and later, select the advanced configuration setting ComplianceRulesWildcardsEnabled. By default, this option is not selected.
NCM uses the Microsoft .NET RegEx engine to evaluate regular expressions. See Regular expression pattern matching examples for some examples of use in NCM. For detailed information about the syntax, see Microsoft's Regular Expression Language Quick Reference.
-
-
If you entered a regular expression, click Regular Expression (Regex). If you entered a simple string, verify that Find String is selected.
Define search conditions using Advanced Config Search
-
Specify whether the rule triggers an alert when the string is found or when the string is not found.
If the search string includes lines that must be included and lines that must not be included, choose the alerting option that is appropriate for the first line. See Example 2.
-
Select Advanced Config Search.
The Advanced Config Search and Search Config File/Block sections are displayed.
-
In the Advanced Config Search section, define the first search string.
Must/Must Not Contain Specify whether the string should be included in the config. String Type Specify whether the string should be evaluated as a regular expression or a simple string.
By default, a simple string can not include the wildcard characters ? and *. To use wildcards, do one of the following:
-
Enter a Regular Expression.
-
In NCM 2023.1.1 and later, select the advanced configuration setting ComplianceRulesWildcardsEnabled. By default, this option is not selected.
String Enter the string to search for.
NCM uses the Microsoft .NET RegEx engine to evaluate regular expressions. See Regular expression pattern matching examples for some examples of use in NCM. For detailed information about the syntax, see Microsoft's Regular Expression Language Quick Reference.
-
-
To build conditions into your search:
-
Click Add Another String.
-
Enter the string and specify the relationship between the lines. (See Examples of search string conditions.)
And/Or Select an operator to define the relationships between strings. Parens Optionally, use parentheses to group strings into conditional relationships.
-
Repeat to add as many conditions as you need to define the rule.
-
-
To search only part of the config:
-
Under Search Config File/Block, select Config block.
-
In the Config block start box, enter a string or regular expression to define the beginning of the block.
Do not use a multiline regular expression to define the beginning of the block.
-
In the Config block end box, enter a string or regular expression to define the end of the block.
If the block contains only one line, enter the macro
${SupportSingleLineMatch}immediately after the regex or string that identifies the end of the block. For example, (depending on the line break characters used in the config), the Config block end box could contain the following to indicate that the block ends at the line break:\r?\n${SupportSingleLineMatch} -
Specify the string type.
-
If you do not want an alert triggered because the block is not found, select the Do NOT trigger alert checkbox.
-
(Optional) Task 3: Define a remediation script
Each rule can include a script to add or remove lines of a configuration to automatically remediate the policy violation.
-
Enter or load a script that makes the required changes to the config.
The remediation script must include CLI statements that run on the relevant devices. When executed, the script runs through the default communication protocol, such as Telnet or SSH.
The script should perform the following tasks in order:
-
Put the device into configuration mode, if needed.
-
Issue a series of config commands.
-
Exit config mode.
-
-
Select a Remediation Script Type. Your selection determines how NCM executes commands against targeted devices to remediate a policy rule violation.
-
CLI allows NCM to use the commands in the script to change the config.
-
Config Change Template launches the Config Change Template wizard to guide you through executing the script.
-
-
For a CLI script, specify the following options:
Option Description Automatically execute this script Select this option if you want NCM to execute the script automatically when a policy violation is found.
Otherwise, you can choose to execute the script when you view the policy report that lists the rule violation.
Be sure to test the script thoroughly before you choose to execute it automatically.
Run script on each config block in violation This option is available only if you selected the option to search a config block rather than the entire config. Select this option if you want to run the script on each config block that violates this rule.
When you select this option, the macro
${ConfigBlockStartLine}is automatically added to the beginning of the script. This macro inserts the entire starting line of the config block.To insert only the part that matches the entry in the Config block start box, replace the default macro with
${ConfigBlockMatchValue}.For example, if the config line is:
Gi1/0/1 admin down down, and the Config block start is^\S+, then:-
${ConfigBlockMatchValue}inserts only the characters before the first space:Gi1/0/1 -
${ConfigBlockStartLine}inserts the entire line:Gi1/0/1 admin down down
Execute Script in Config Mode Select this option if you want NCM to put the device in config mode before executing the script. -
Task 4: Test and save the rule
Test the rule to verify that it finds policy violations as expected.
If the rule includes multiple lines containing regular expressions, SolarWinds recommends testing each regular expression individually before you test the rule as a whole. You can:
Use an online RegEx tester to test each expression.
Include only one of the regular expressions in a rule, and use NCM to test that rule against your configs.
-
Click Test to validate the rule against a device configuration.
-
Do one of the following:
-
To paste the config contents you want to test the rule against, choose Paste a config block.
-
To test against an uploaded config file, choose Select a config (selected by default).
-
-
Paste a config block or select a config to test the rule against.
-
Click Test Rule Against Selected Config.
If the config violates the rule, the Results panel indicates which search strings violated the rule and whether the violation occurred because the string was found or not found.
If the violation occurred because the string was found, you can click the arrow to display the line number in the config file.

-
Click Select Different Config to test the rule against another config.
SolarWinds recommends testing the rule against at least two configurations: one known to comply with the rule, and another known to violate it.
If you are testing a regular expression that uses the $ operator, be aware that the downloaded config can contain special non-printable characters that prevent the $ operator from matching the line end. To determine if there are non-printable characters at line ends, paste lines from the config into a plain text file in a text editor. If you see extra, empty lines in the text file that are not visible in the config, those lines probably contain non-printable characters.
-
When you have finished testing, click Close.
-
Click Submit to save the rule in the selected folder.
Examples of search string conditions
The following sections show how to define some simple conditions, and how NCM evaluates each example.
Example 1: Config must contain at least one of multiple strings
In this example, a config must contain at least one of the following strings:
Must contain string1
OR must contain string2
OR must contain string3
NCM reports a rule violation if the config does not contain any of the strings.

Example 2: A config must contain one string and must not contain another
In this example, the first string is required, but the second cannot be included.
Must contain string1
AND must not contain string2
NCM reports a rule violation if:
-
A config does not contain
string1. -
A config contains both
string1andstring2.

Example 3: Config must contain at least one string in a group and a string outside the group
This example uses parentheses to group the first two strings. A config must contain at least one of the strings in the group, as well as the third string.
(Must contain string1
OR must contain string2)
AND must contain string3
NCM reports a rule violation if:
-
A config contains either
string1orstring2, but does not containstring3. -
A config contains
string3, but does not contain eitherstring1orstring2. -
A config does not contain any of the strings.

Edit a rule
Edit a rule to reflect policy changes or to refine the search string or remediation script. For example, if policy reports return false positives on violations, edit the rule to improve the search string.
-
Click My Dashboards > Network Configuration > Compliance.
-
Click Manage Policy Reports.
-
Click the Manage Rules tab.
-
Select a rule, and click Edit.
-
Edit values, and click Submit.
Delete a rule
-
Click My Dashboards > Network Configuration > Compliance.
-
Click Manage Policy Reports.
-
Click the Manage Rules tab.
-
Select a rule, and click Delete.
-
Click Yes.
Customize alert level descriptions for rules
NCM provides three levels to specify the severity of a rule violation. By default, these levels have the following descriptions.
| Level | Default Description |
|---|---|
| 1 | Informational |
| 2 | Warning |
| 3 | Critical |
You can customize the description of each level.
-
Click Settings > All Settings.
-
Under Product Specific Settings, click NCM Settings.
-
In the Compliance Policy Report Management section, select Manage Violation Levels.
-
In the text field for the level that you are changing, replace the word describing that level.
-
Click Submit.
Next steps
After you define rules, you can create a policy and then create a policy report.