
Configure LDAP for SEM
In SEM, you can create multiple LDAP connections.
In SEM 2026.4 and later, LDAP connections must use SSL encryption (LDAPS). When you upgrade, SSL encryption is turned on for all existing LDAP configurations. If you currently connect to your LDAP server without encryption (typically on port 389), make sure LDAPS (typically port 636) is enabled and reachable on the LDAP server before you upgrade, otherwise LDAP users cannot log in to SEM.
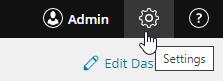
- Click the settings icon on the upper right.
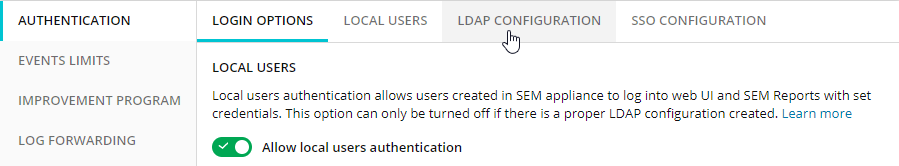
- Select Authentication > LDAP Configuration.
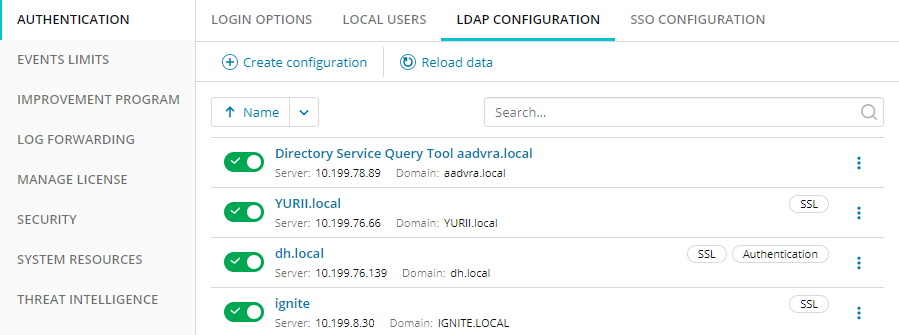
If any LDAP configurations have already been created these are displayed.
- Click Create configuration.
The Create LDAP Configuration dialog is displayed.
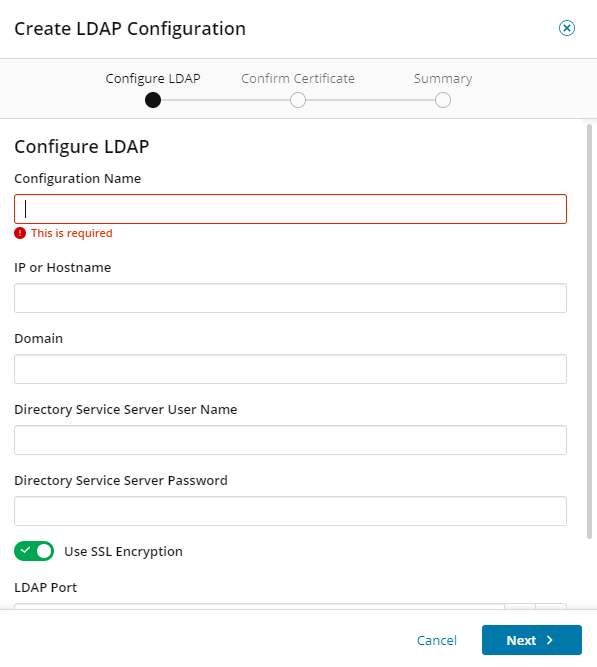
- Enter the following information:
Field Description Configuration Name Enter a friendly name of your choosing for the LDAP configuration. IP or Hostname Enter the IP address or host name of your LDAP server.
Domain Enter the fully-qualified domain name for the account store. Directory Service Server User Name
Use the format account_name@example.com.
SolarWinds recommends using a Directory Service account to prevent integration issues if the software license expires. The user name does not require special privileges (such as Domain Admin) to be a Directory Service user.
Directory Service Server Password Enter the password for the user account. Use SSL Encryption SEM uses the transport layer security protocol (LDAPS) for a secure connection to the LDAP server. This option directs traffic from the SEM VM to a designated server (usually a domain controller) for use with the Directory Service tool.
In SEM 2026.4 and later, this option is selected by default and cannot be cleared. Non-encrypted LDAP connections are no longer supported.
LDAP Port The default port for LDAPS is 636. Make sure LDAPS is enabled on your LDAP server and that SEM can reach it on this port.
Use for Authentication Select, then click Next if you wish to use Advanced Settings shown below. Domain Aliases (Optional) Specify any Domain Alias names that should be authenticated using this LDAP configuration. (The role/group names configured on this page will also apply.) NetBIOS Names (Optional) Specify any NetBIOS names that should be authenticated using this LDAP configuration. (The role/group names configured on this page will also apply.) Admin Group (Optional) Specify the DS group in Active Directory to use for the SEM administrator role. If you do not specify a name, the default ROLE_LEM_ADMINISTRATORS group is used. Alerts Only Group (Optional) Specify the DS group in Active Directory to use for the SEM auditor role. If you do not specify a name, the default ROLE_LEM_AUDITOR group is used. Guest Group (Optional) Specify the DS group in Active Directory to use for the SEM guest role. If you do not specify a name, the default ROLE_LEM_GUESTS group is used. Notify Only Group (Optional) Specify the DS group in Active Directory to use for the SEM notifications role. If you do not specify a name, the default ROLE_LEM_CONTACTS group is used. Reports Group (Optional) Specify the DS group in Active Directory to use for the SEM reports role. If you do not specify a name, the default ROLE_LEM_REPORTS group is used. - Click Next.
-
The SSL certificate of the LDAP server is shown. Click I trust this certificate to confirm.
SEM trusts the root certificate authority (CA) in the certificate chain presented by the LDAP server (or the farthest CA in the chain if the root is not included), not only the server (leaf) certificate. As a result, you do not need to trust the certificate again when the LDAP server certificate is renewed by the same CA.
If you enter an IPv6 address in the IP or Hostname field, the LDAP server certificate must include that IPv6 address as a subject alternative name (SAN).
- Click Finish to create this configuration.
- Configurations can be sorted by name. For each configuration, the name, server, and domain are displayed, plus flags to show if they use SSL and/or used for Authentication.
Enable and disable LDAP configurations
Configurations are enabled as soon as they are created.
Use the toggles to disable or enable individual LDAP configurations.
A warning message is displayed if you disable a configuration informing you that users will be unable to log on from that domain and any logged-in users from that domain will be immediately logged out.
Edit or delete an LDAP configuration
- To edit or delete an LDAP configuration, click on the vertical ellipsis icon after the configuration.

- Click Edit to display the Configure LDAP details for this configuration (which can now be saved) or click Delete to remove this configuration.